Swift action to secure UK supermarket controls
20th November 2026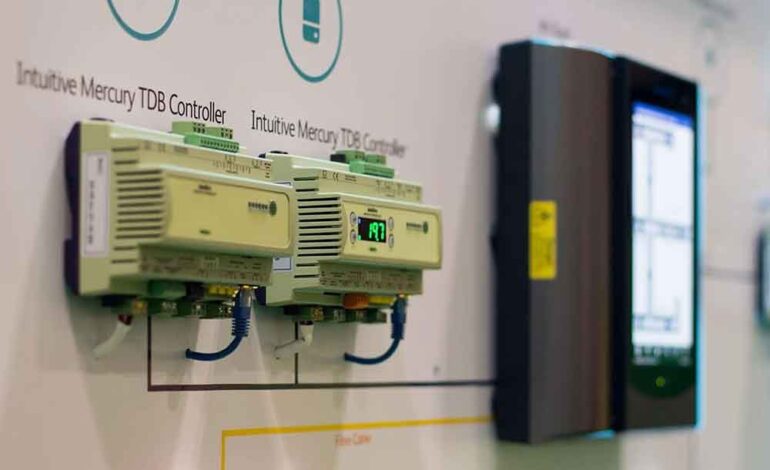
UK: Glasgow-based controls manufacturer Resource Data Management (RDM) has released new firmware as part of a major move to secure its UK supermarket controllers from possible cyber attack.
While RDM, the dominant supermarket controls supplier in the UK, had so far avoided the recent cyber attacks experienced in Europe, security companies did discover vulnerabilities in its controllers. However, the issues were harder for hackers to find than the Danfoss vulnerabilities exposed in the recent French attacks.
While many of the significant operators out of the thousands of exposed RDM controllers have been contacted and advised to apply the latest firmware. The issue is said to have been largely mitigated, though smaller cold chain operators may still be exposed. The UK’s National Cyber Security Centre and the British Retail Consortium have been sharing intelligence, but the supply chain for chilled and frozen food is complex and extensive.
Users are also advised to verify that the RDM controllers are not available from the public internet. Common issues are said to include the use of cellular modems on the public internet, so using a VPN or private APN is also advised.
According to UK-based cyber security company Pen Test Partners, RDM was first alerted to “a significant vulnerability” in its controllers by Gary Turner and Neil McCourt at Yorkshire-based fridge telemetry and control systems company Omega Solutions. Working to validate the findings with Andrew Tierney of UK cyber security company Pen Test Partners, they discovered a number of additional vulnerabilities.
Omega alerted the NCSC and, together with the British Retail Consortium, DEFRA, the Food Standards Agency and others, a mass effort was initiated to contact supermarkets and their supply chains, locate exposed controllers and mitigate the issue.