French supermarkets using date-based passwords
16th October 2026
FRANCE: A new report reveals that prior to Sunday night’s cyberattack on French supermarket controllers most operators were using an admin password based on the current date.
Censys, a US cybersecurity company, reviewed every Danfoss StoreView control panel found online and identified the version running on each host. Before the attack, 61% of these devices were in France, and most ran a version where the admin password could be derived from the current date.
This is seen as a critical security vulnerability as the password is generated using a predictable mathematical formula, pattern, or text format based on the calendar date. It enables hackers, who know or guess the algorithm, to easily calculate the password for any given day.
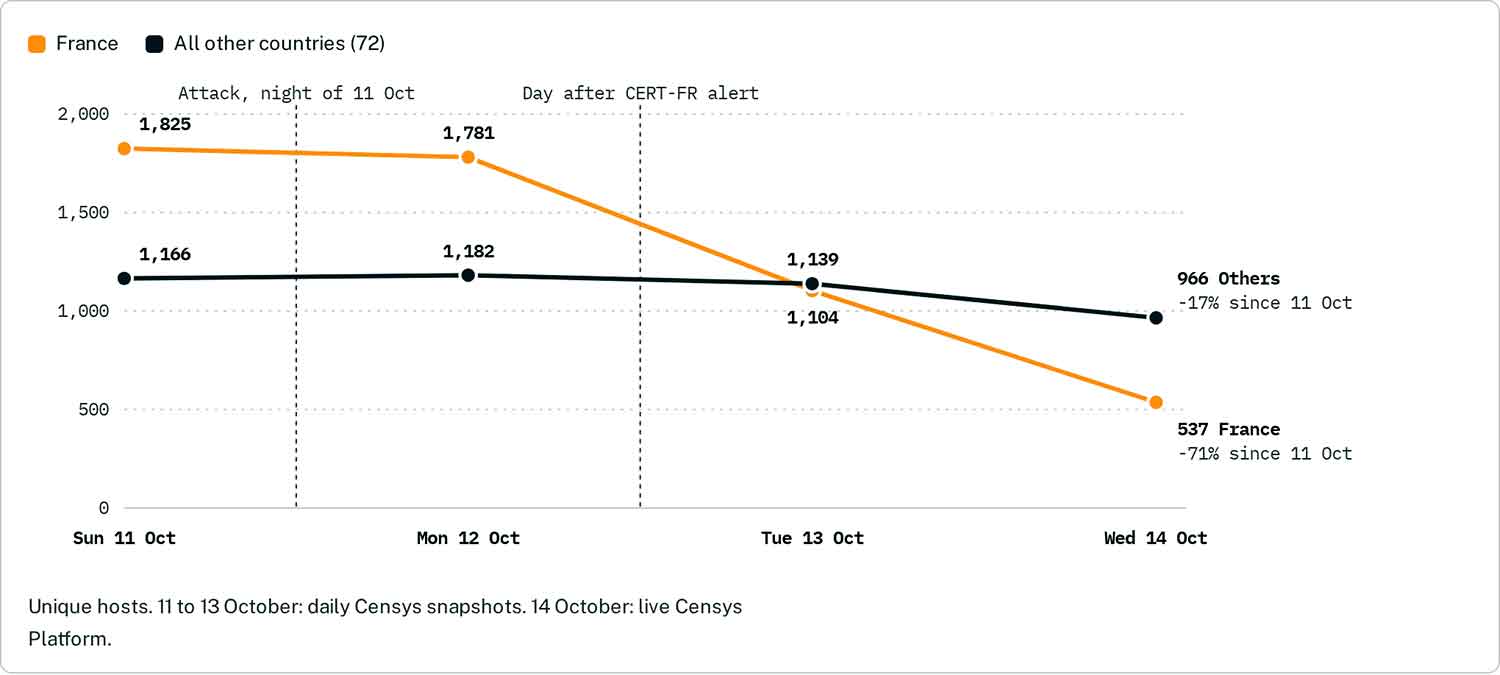
On October 11, prior to the attack, Censys identified 2,991 hosts with a Danfoss StoreView control panel. The majority of these, 1,825, were in France, with Belgium, the next most exposed country at 240.
The reaction to the attack is clear: the number of StoreView control panels in France dropped from 1,825 hosts before the attack to 537 on October 14.
According to Censys data, operators didn’t appear to be patching their controllers but simply taking them off the Internet; both patched and unpatched controllers disappeared at the same rate.